
WordPress powers a massive share of the web, which also makes it the most frequently targeted CMS. In 2026, the majority of successful attacks still exploit outdated plugins, weak credentials, and missing basic hardening rather than sophisticated zero-days in WordPress core.
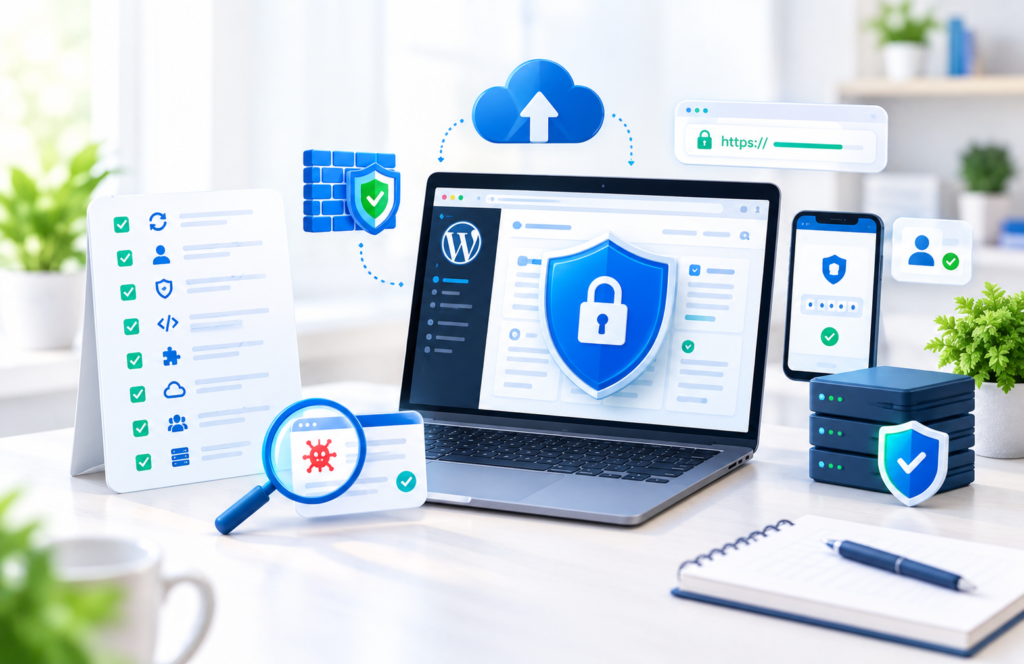
This WordPress security optimization 2026 guide gives you a practical, prioritized WordPress security checklist and WordPress hardening checklist you can implement today. Follow these WordPress security best practices 2026 to significantly reduce your risk of compromise.
1. Keep Everything Updated Automatically
The single biggest cause of hacked WordPress sites remains unpatched software. Enable automatic updates for WordPress core minor releases and carefully review major updates and plugin/theme updates.
Outdated plugins and themes account for the vast majority of vulnerabilities. Schedule regular checks and remove anything no longer needed. This simple step closes the majority of known attack vectors.
2. Strengthen Login Security
Brute-force and credential-stuffing attacks remain extremely common.
- Use strong, unique passwords generated by a password manager for every administrator and editor account.
- Enable two-factor authentication WordPress (app-based 2FA preferred over SMS).
- Limit login attempts and consider renaming or protecting the login page.
- Disable XML-RPC if you do not need it, as it is frequently abused for amplification attacks.
These measures stop the majority of automated login attacks.
3. Install and Configure a Reliable Security Layer
Choose one primary security solution rather than stacking multiple overlapping plugins. Popular options in 2026 include Wordfence, Patchstack, Sucuri, Jetpack Protect, and MalCare.
A good setup typically includes:
- Web Application Firewall (WAF)
- Malware scanning and file integrity monitoring
- Login protection and rate limiting
- Vulnerability alerts or virtual patching
A properly configured WordPress WAF and malware scanner form the core of modern WordPress security optimization.
4. Harden File Permissions and Configuration
Set correct file permissions (directories 755, files 644, and stricter for wp-config.php). Disable the theme and plugin file editor in the dashboard by adding DISALLOW_FILE_EDIT to wp-config.php.
Protect wp-config.php, keep security keys (salts) unique and fresh, and ensure HTTPS is forced site-wide with proper security headers (HSTS, X-Frame-Options, Content-Security-Policy where possible).
5. Audit and Minimize Plugins and Themes
Every plugin increases your attack surface. Conduct a quarterly WordPress plugin audit: remove unused plugins completely (deactivating is not enough), check last-updated dates, and prefer actively maintained plugins from trusted developers.
Fewer, well-maintained plugins dramatically improve WordPress plugin security.
6. Implement Proper Backups and a Recovery Plan
Automated daily off-site backups are non-negotiable. Store them separately from your hosting account and test restores regularly.
Create a simple breach recovery plan so you know exactly how to isolate the site, clean malware, restore from a clean backup, and communicate if needed. A backup you have never tested is not a reliable control.
7. Apply Additional Hardening Measures
- Use the principle of least privilege for user roles.
- Hide or remove WordPress version information where practical.
- Disable directory listing.
- Restrict REST API user endpoints if not required.
- Monitor activity logs for unusual admin or file changes.
- Keep PHP on a currently supported version (8.3 or 8.4 preferred in 2026).
8. Choose Secure Hosting and Monitor Continuously
Secure WordPress hosting with isolation, server-level scanning, and good support makes a measurable difference. Combine this with ongoing monitoring so you detect issues early rather than learning about a compromise from Google or your visitors.
Ongoing Maintenance Is Essential
WordPress security optimization is not a one-time project. Schedule monthly or quarterly reviews of updates, plugins, users, backups, and security plugin reports. New vulnerabilities appear regularly, and the median time from disclosure to mass exploitation can be measured in hours.
By following this WordPress security checklist and treating security as an ongoing process, you move your site from an easy target to a significantly harder one. Most successful attacks in 2026 still succeed because basic hygiene was missing — not because of advanced zero-days.
If you manage multiple WordPress sites or want professional help implementing a complete hardening and monitoring setup, a specialist who combines technical SEO, performance, and security work can save considerable time and reduce risk.
Start with the highest-impact items today: updates, strong credentials with 2FA, a quality security plugin, and tested backups. These four steps alone will protect the majority of WordPress sites from the most common threats in 2026.